

Velogic is looking for a Cybersecurity & Awareness Officer to manage cybersecurity risks, protect IT systems and data, respond to security incidents, and promote cybersecurity awareness across the Group.
Duties & Responsibilities:
•Implement, maintain and continuously improve the Group’s cybersecurity framework, policies, standards and risk management practices across countries and business units.
•Coordinate and oversee cybersecurity operations with internal teams and external service providers, covering endpoint, network, email, cloud, identity and access security, MFA, VPN and other security technologies.
•Establish and manage the vulnerability management programme, including assessments, risk classification, remediation tracking, penetration testing and timely resolution of critical vulnerabilities.
•Coordinate the response to cybersecurity incidents, ensuring appropriate escalation, investigation, documentation, corrective actions, post-incident reviews and lessons learned.
•Monitor security alerts, emerging cyber threats and security events, and coordinate appropriate preventive and corrective measures with IT teams and security partners.
•Ensure effective controls around user access, privileged accounts, joiner/mover/leaver processes, dormant accounts and periodic access reviews, in collaboration with HR and IT.
•Assess cybersecurity risks relating to suppliers and technology partners, contribute to business continuity and disaster recovery exercises, and coordinate consistent cybersecurity standards across the Group’s international operations.
•Develop cybersecurity dashboards and KPIs covering incidents, vulnerabilities, patching, MFA, awareness, audits, risks and other key security indicators, providing management with clear visibility of the Group’s cybersecurity posture
Qualification & Competencies:
•Bachelor’s degree in Cybersecurity, IT, Computer Science, Information Systems or a related discipline.
•3+ years’ experience in IT, Information Security or Cybersecurity, with relevant professional experience considered in lieu of specific qualifications.
•Professional certifications such as CISSP, CISM, CISA, Security+, CEH or equivalent are an advantage.
•Proven experience in cybersecurity risk management, vulnerability management and incident management.
•Strong understanding of network, infrastructure, endpoint, cloud and Microsoft security environments.
•Experience in cybersecurity awareness programmes and coordinating security activities across multiple sites/countries will be an advantage.
•Willing to work across different departments and learn the business from the ground up.
•Excellent communication Skills
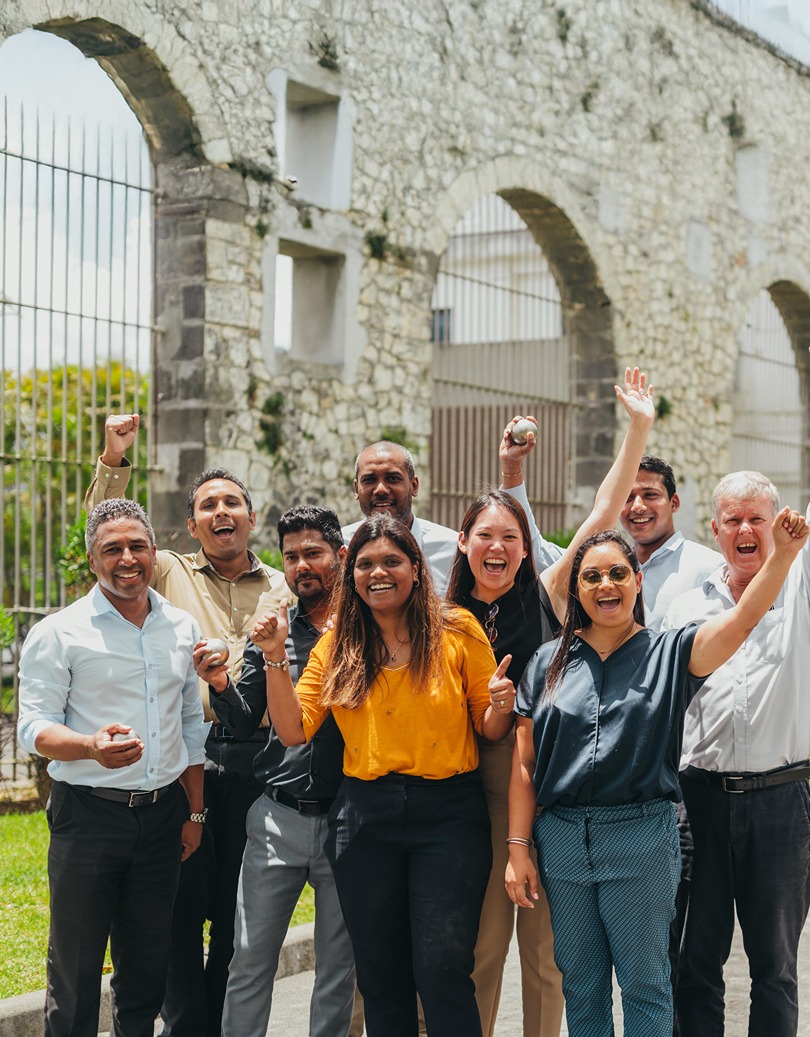
At ER, our people are the driving force behind our purpose: Igniting Today, for a better Tomorrow.
Joining the ER Group means being part of a team of more than +12,000 professionals drawing strength from their diversity, expertise, synergy, and international alliances that help us build a stronger, borderless future.
- ER Agri
- Agrïa
- ER Commercial